PDE catalogue
Product identity, batches, markets, importers, support end date.
Product
Crado AI is where a manufacturer keeps evidence: what you make, what it is made of, which gaps you close, and how you notify an actively exploited vulnerability.
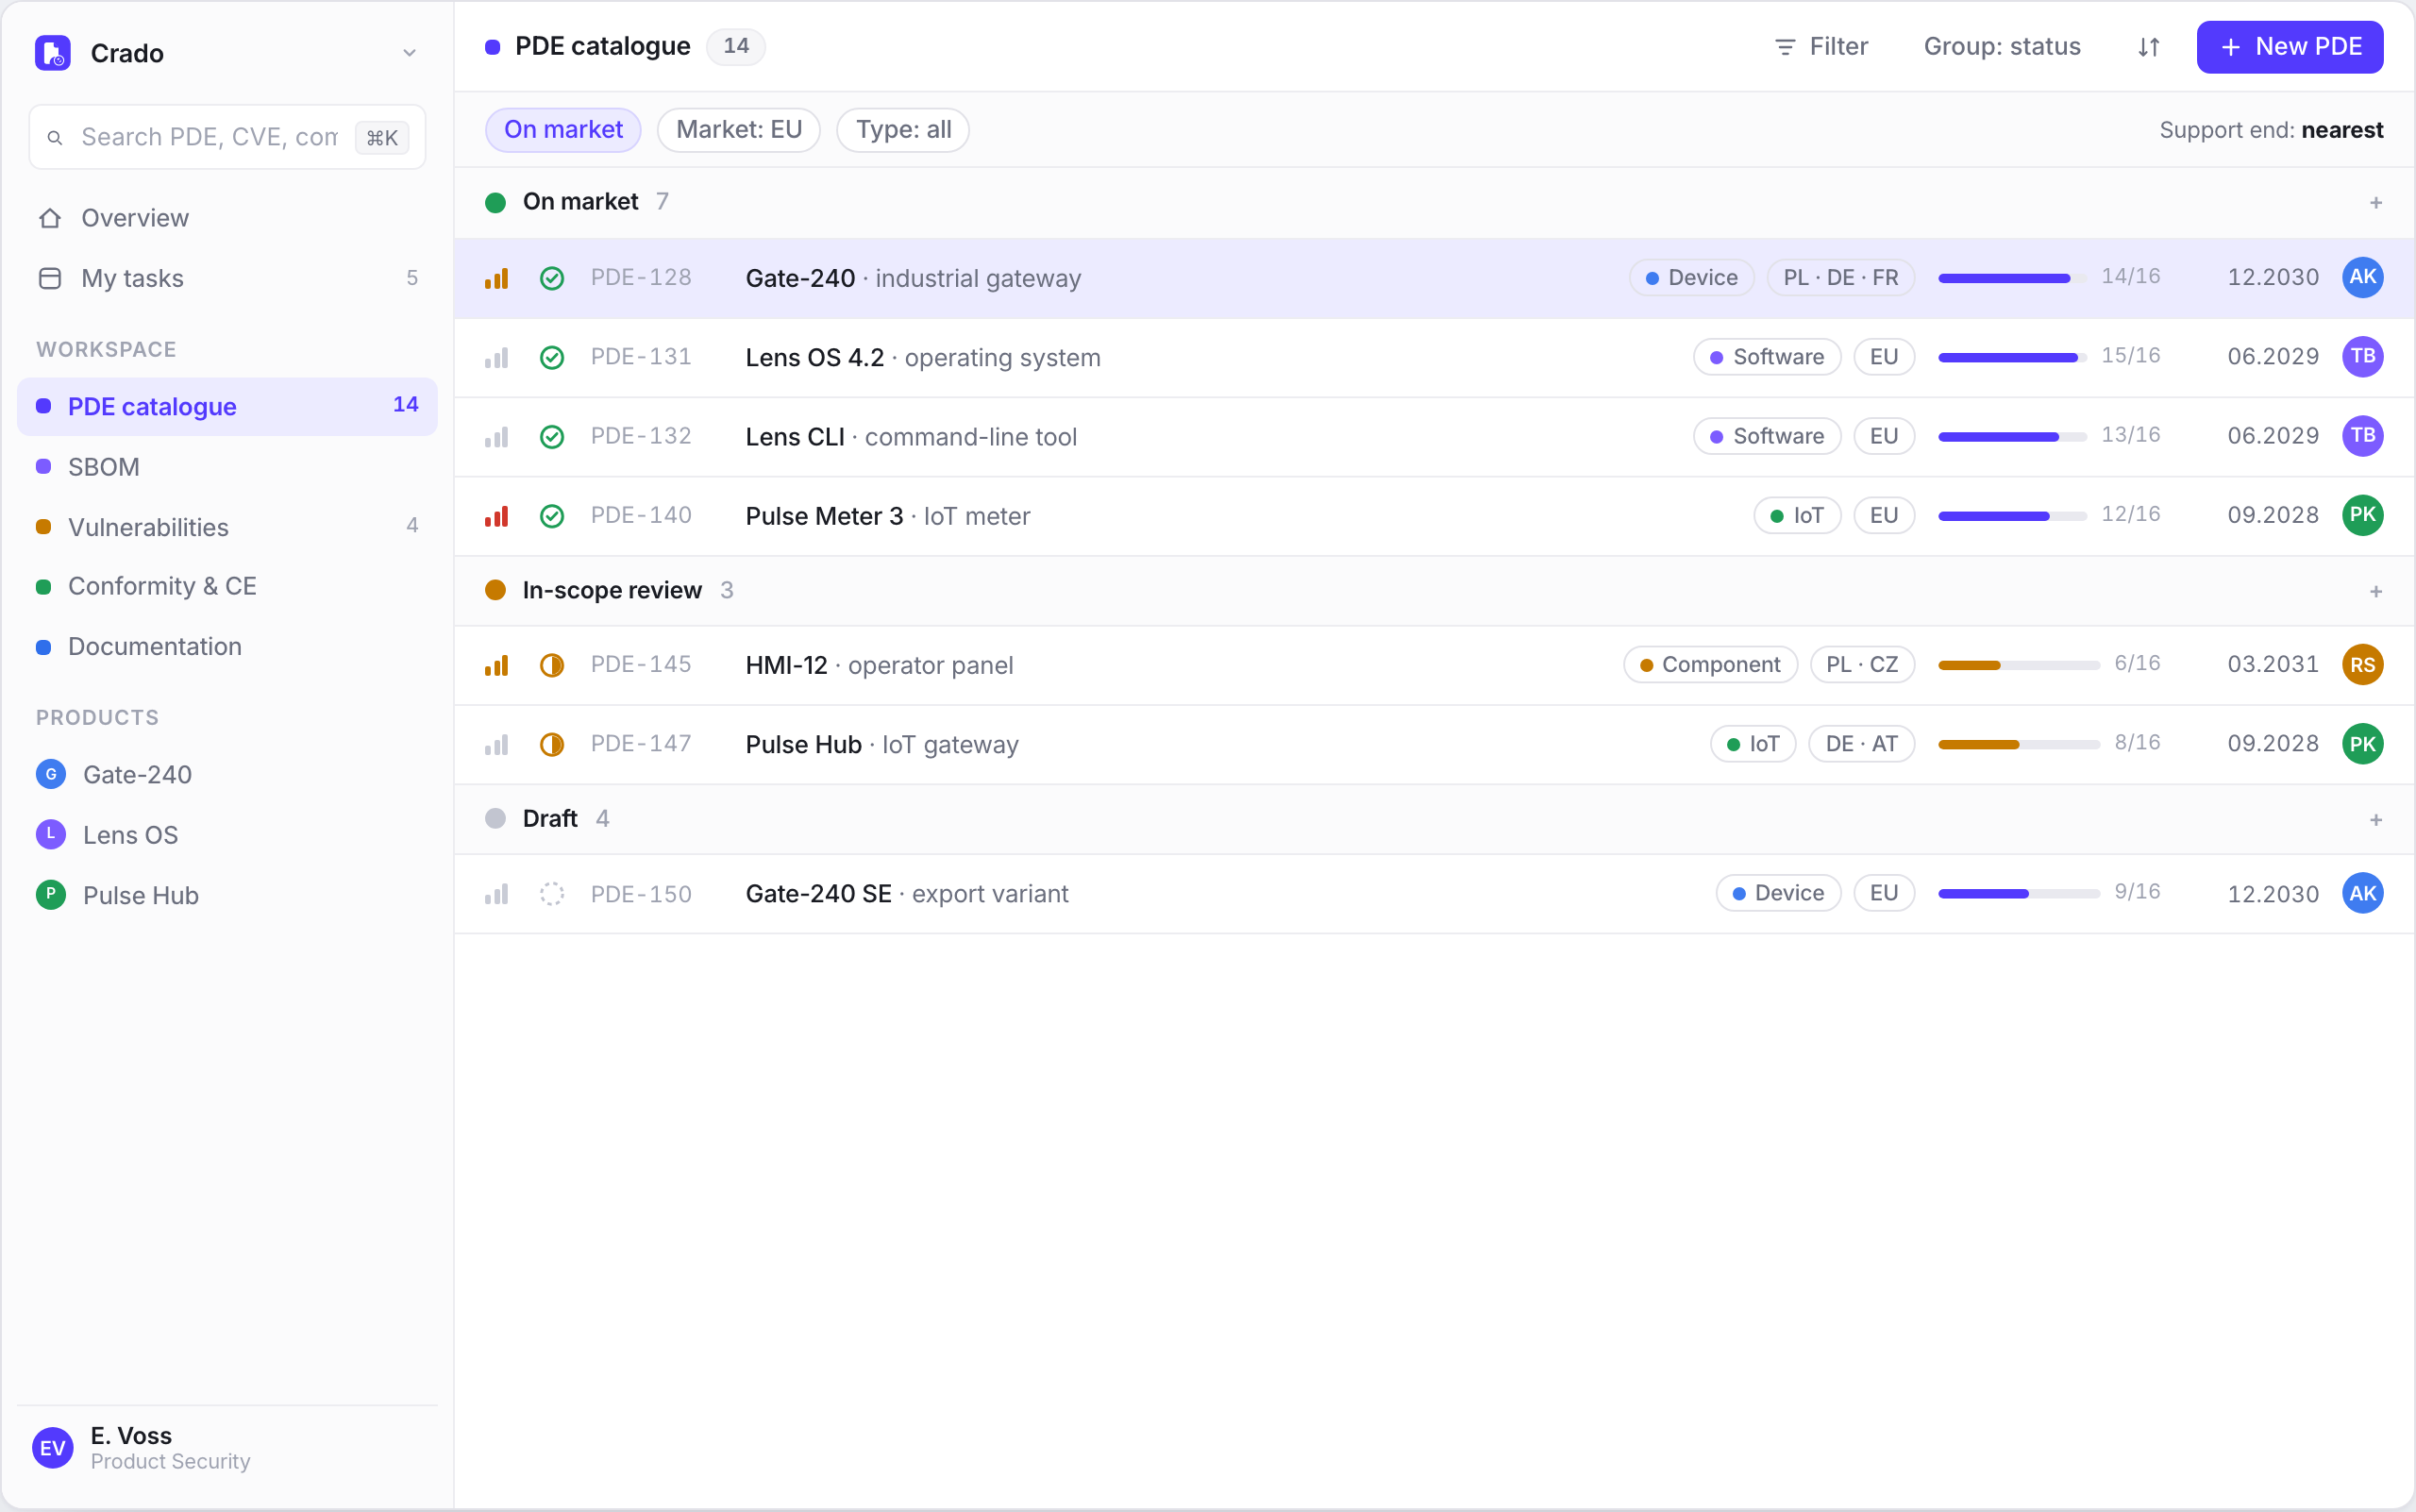
A PDE catalogue with version, market and the date you made it available.
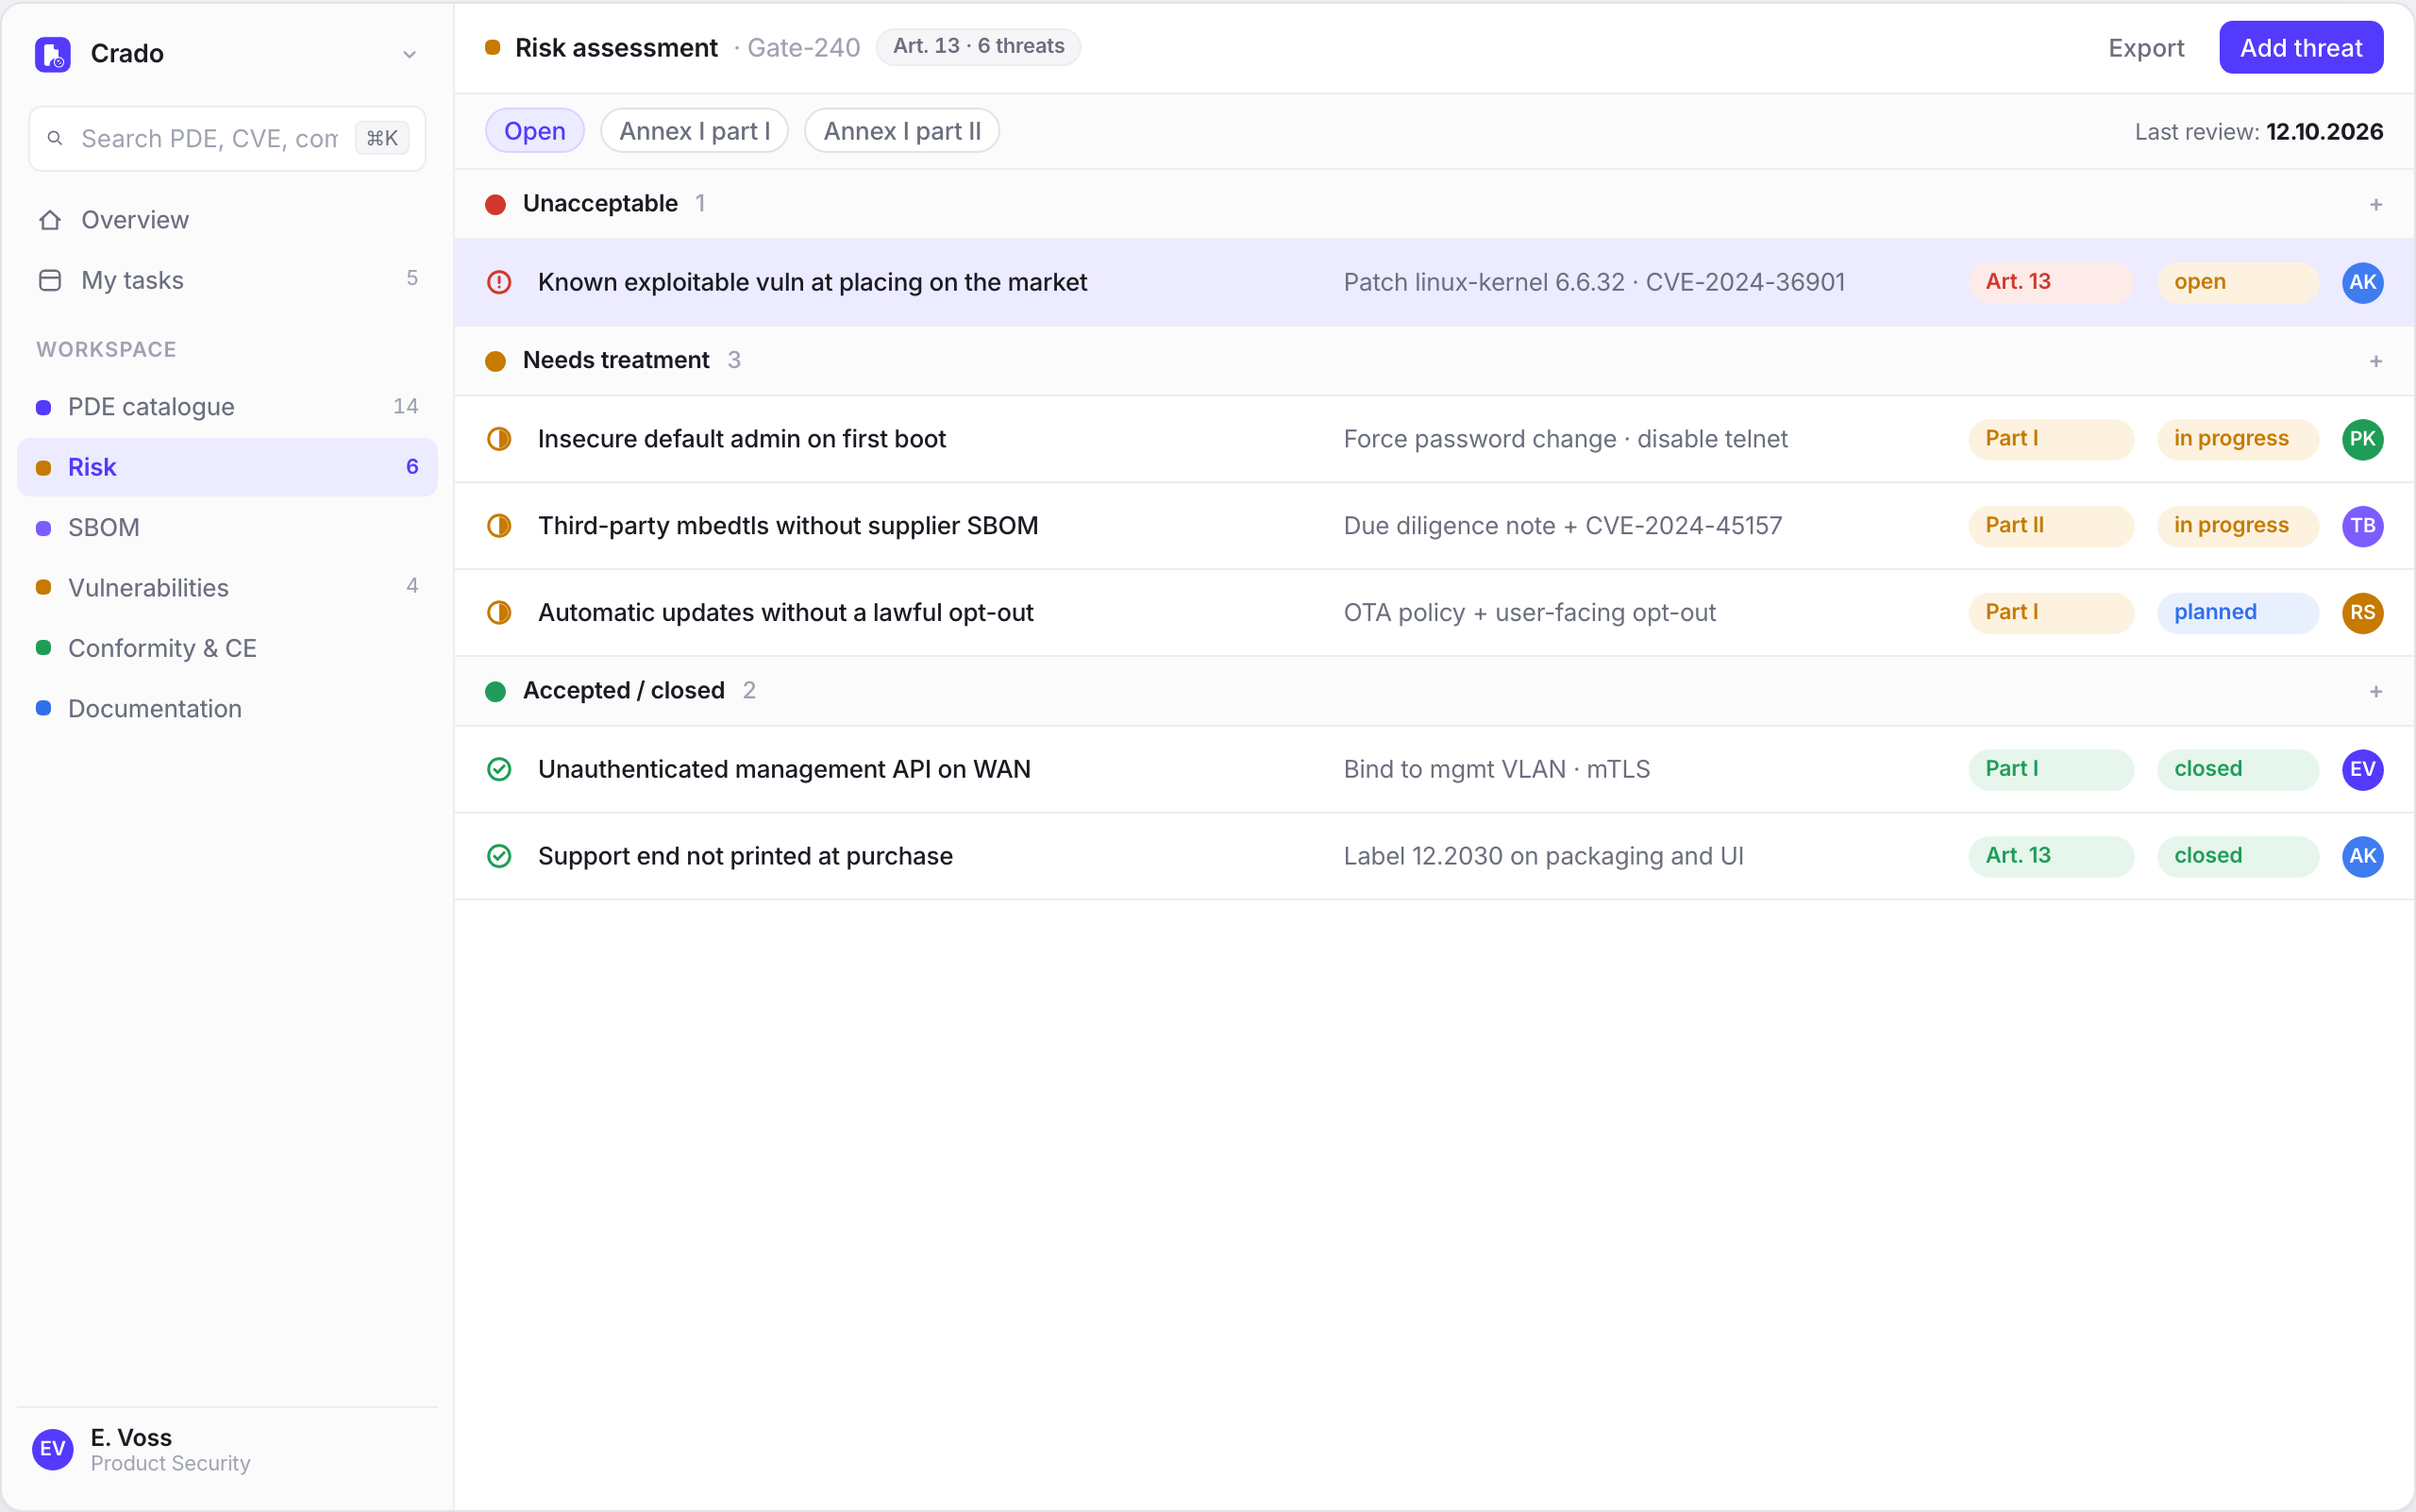
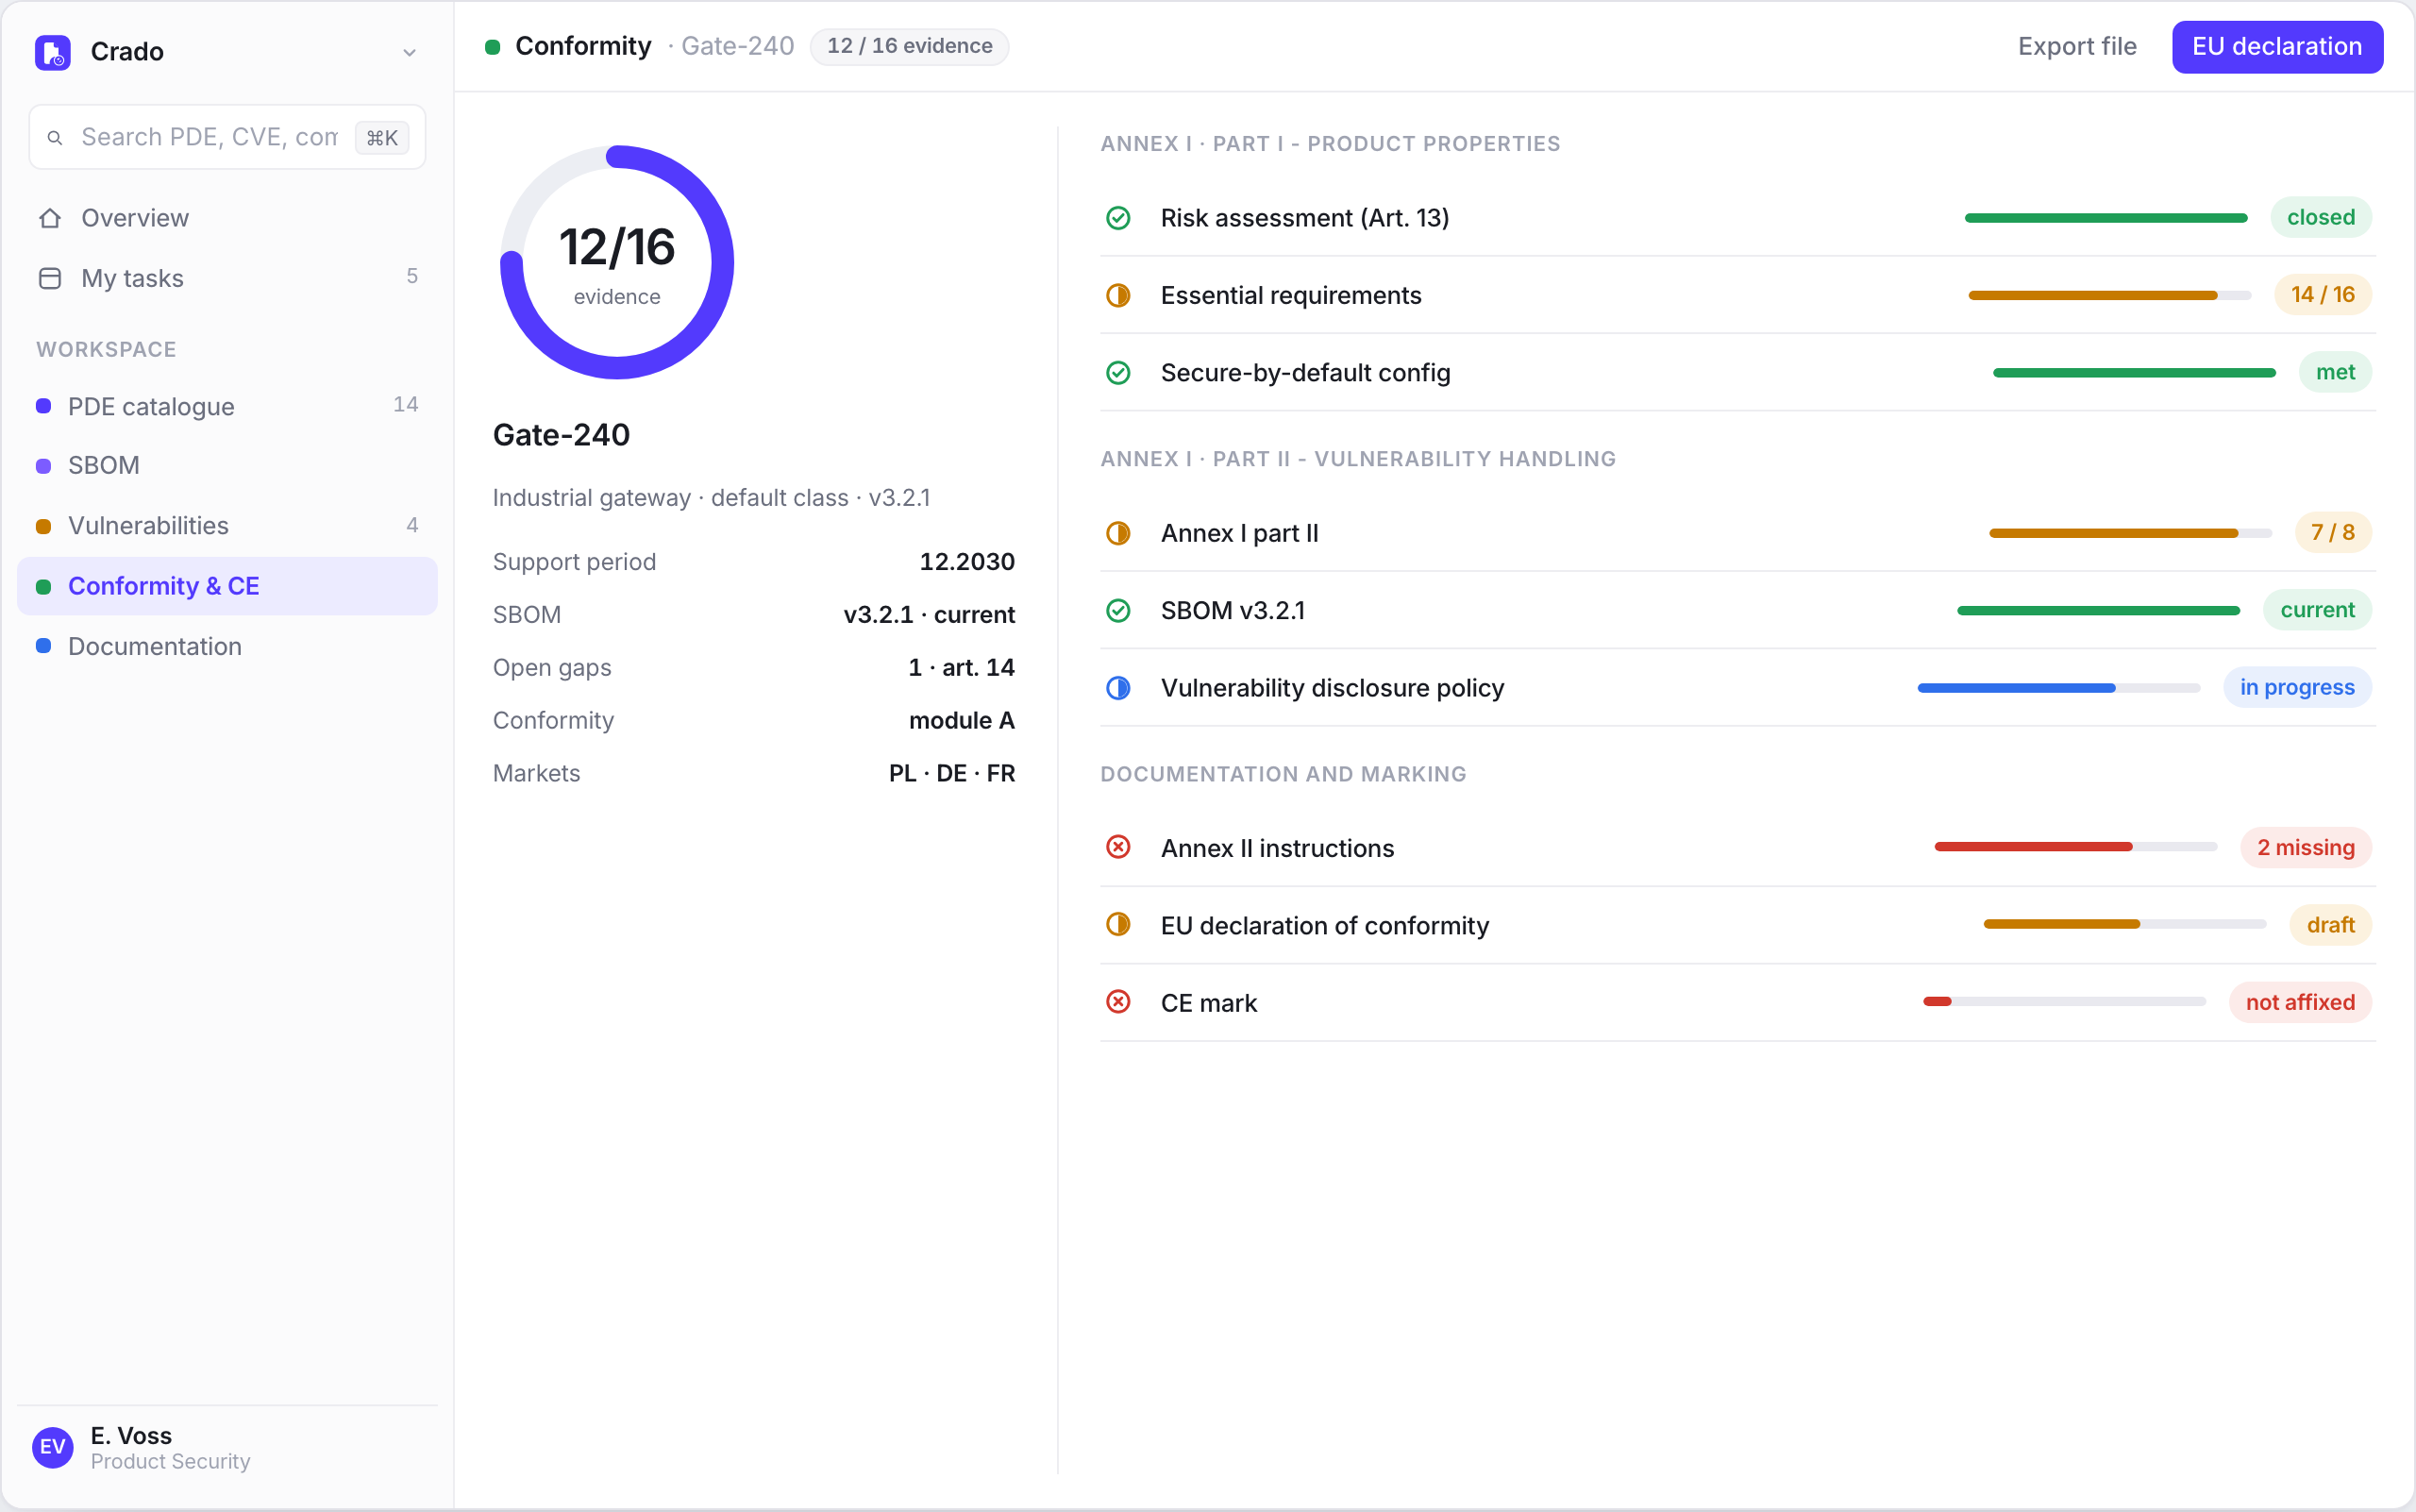
Risk assessment and Annex I on each product, not in a side spreadsheet.
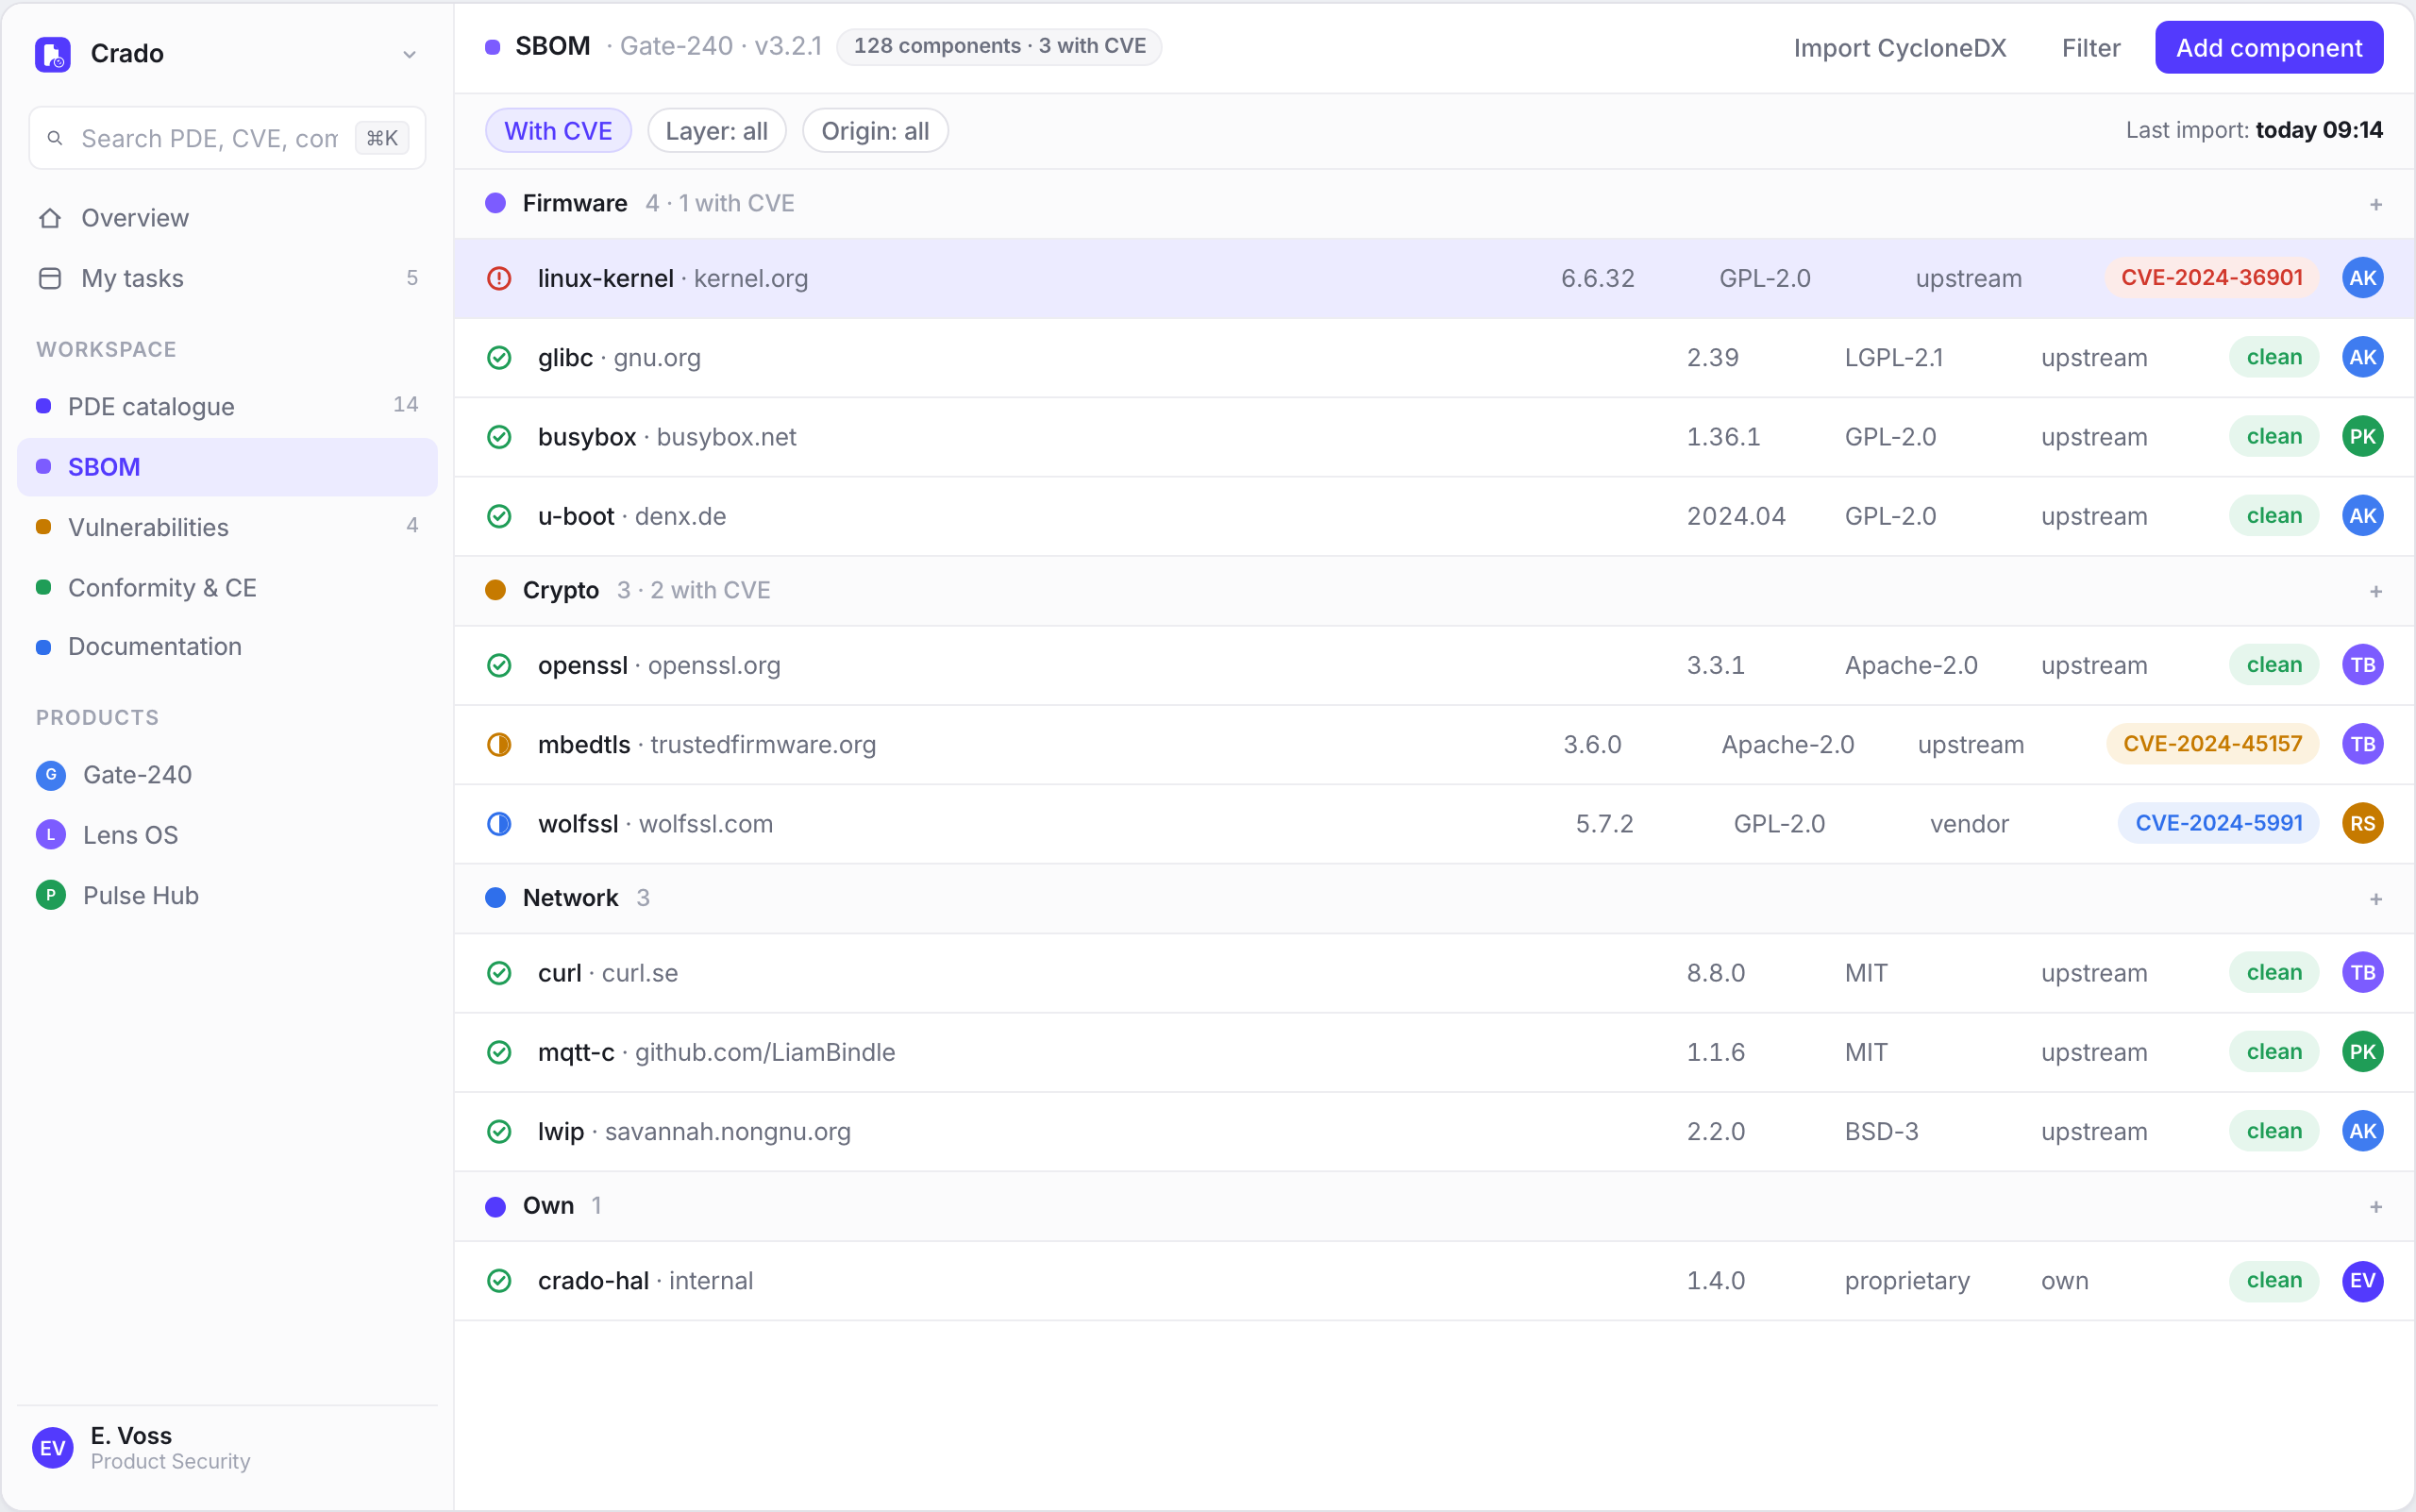
Own and third-party components, with due diligence on suppliers.
Vulnerabilities, updates and Article 14 notifications on a 24h / 72h clock.
Documentation, EU declaration, mark. Then post-market surveillance.
Product identity, batches, markets, importers, support end date.
The regulation applied per product, not once for the whole company.
Product properties and vulnerability handling, tied to risk.
Components, versions, source, links to CVE.
Early warning, full notification, final report.
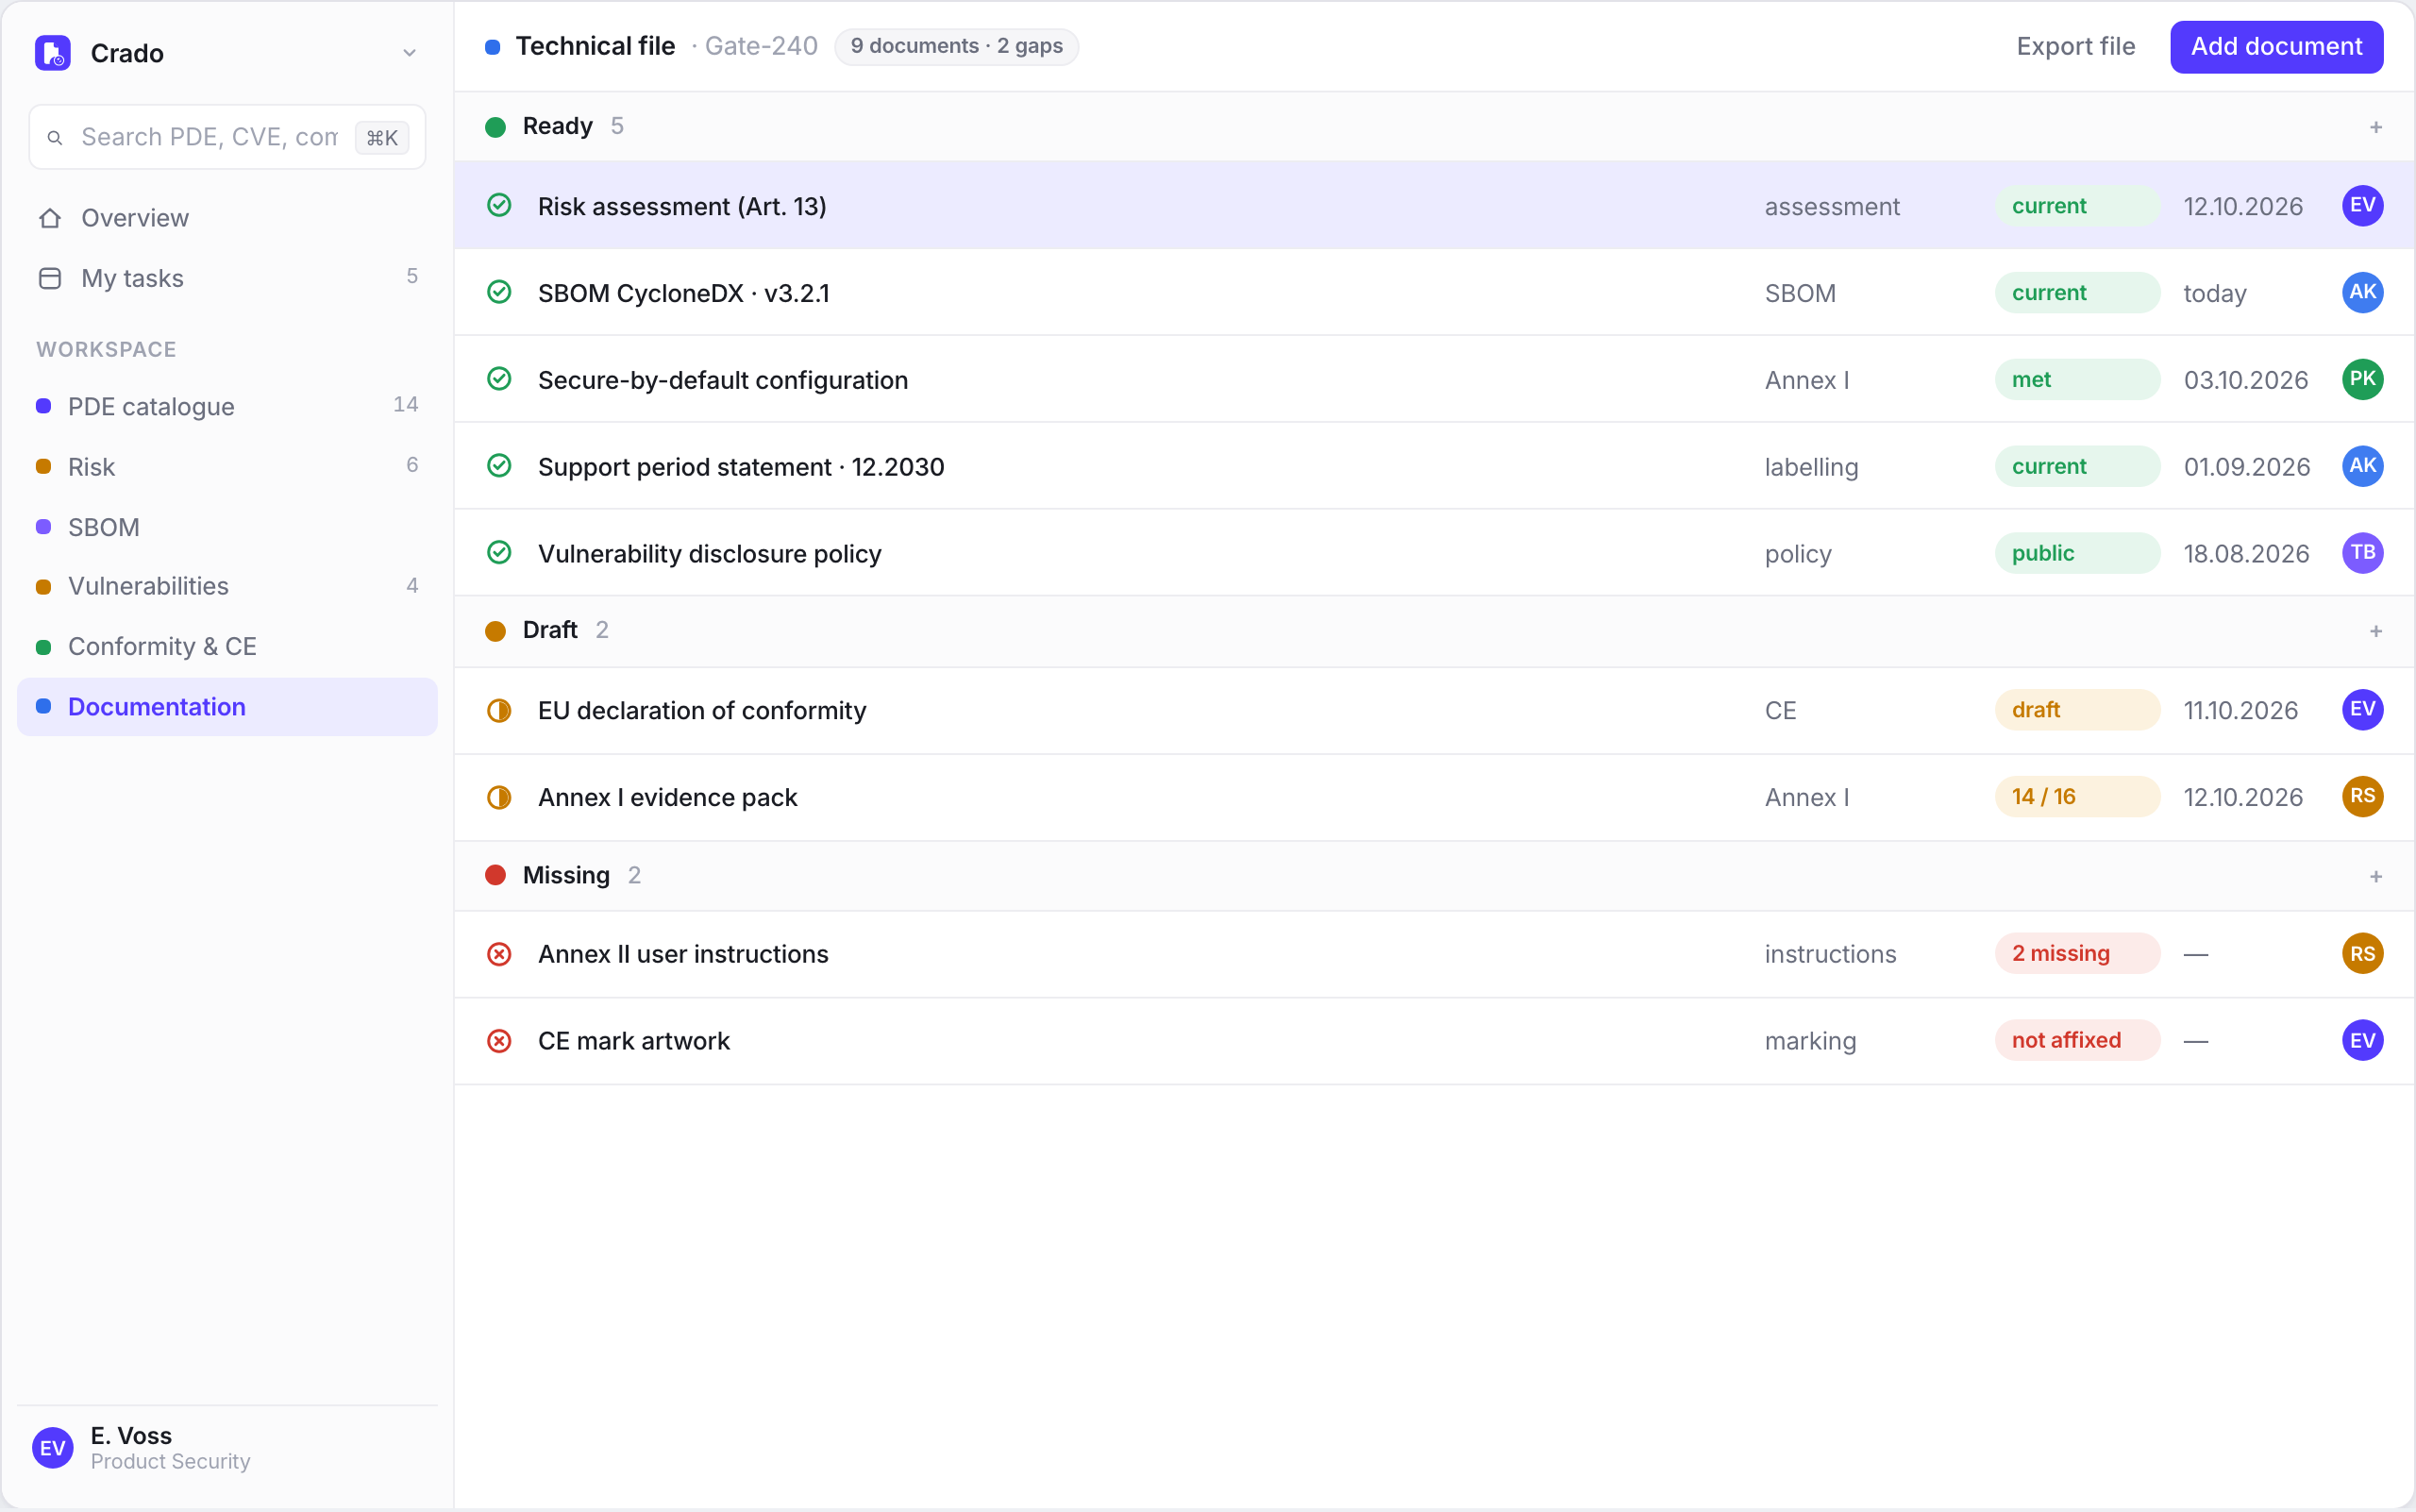
What an authority can demand before the product is placed on the market.
24h
Early warning from the moment you know of an actively exploited vulnerability or a severe incident.
72h
Full notification. One channel (SRP), to the CSIRT of the main establishment, and to ENISA.
14 days / 1 month
Final report: 14 days after a fix for a vulnerability, one month after the 72h notice for an incident.
Installed on the customer infrastructure. Backups, identity and network stay in your standard. There is no SaaS plan.
Twenty minutes. No public price list. A quote after the call, for an on-premise deployment.
Book a call